Campaigns arrive as drafts
The create tool only ever produces a draft. An assistant can build the whole campaign — audience, template, subject — and still cannot be the thing that decides to send it.
Connect Claude — or any assistant that speaks the Model Context Protocol — to your QuickGrow account. It can look up contacts, read a campaign report, draft a campaign and switch an automation on. It cannot send anything to your customers unless you say yes to that exact send, in the moment.
→ get_campaign_report
  { "brand_id": "brd_7", "campaign_id": "cmp_31" }

← { "sent": 1240, "opened": 402, "clicked": 96 }

→ send_campaign
  { "brand_id": "brd_7", "channel": "EMAIL",
    "campaign_id": "cmp_44" }

← requires_confirmation: true
  "This will send “Eid Offer” to about
   1,240 recipients. Show the user first."
  confirm_token: “…”  (10 minutes)
There is no cut-down agent API. Each tool calls the service that powers the equivalent screen in QuickGrow, so what an assistant sees is what you see — the same brands, the same permissions, the same data.
Every tool call clears four checks before it runs: the scope the connection carries, a per-minute rate limit, a one-time approval you gave for that capability, and — for anything that changes something — an audit entry naming the client that made the call.
| Reading | Creating a draft | Sending or scheduling | |
|---|---|---|---|
| A scope on the connection | Yes | Yes | Yes |
| A one-time approval you give per capability | No | Yes | Yes |
| A fresh yes for this exact campaign | No | No | Yes |
| Written to your audit trail, naming the client | No | Yes | Yes |
| Calls allowed per minute, per connection | 60 | 10 | 10 |
Ask it to send a campaign and the first call does not send anything. It returns a preview — the campaign name, its status, the subject, the from address and roughly how many people would receive it — plus a one-time token. The assistant is instructed to show you that preview and wait. Only a second call carrying the token actually sends.
→ send_campaign
  { "brand_id": "brd_7",
    "channel": "EMAIL",
    "campaign_id": "cmp_44",
    "confirm_token": "…" }

← { "id": "cmp_44", "status": "SENDING" }

# audit trail
  mcp.send_campaign  campaign cmp_44
  via mcp · client: Claude Desktop
The connection is a standard sign-in, not a secret you copy around. You approve it as yourself, with your own permissions, and you can take it away in one click.
A conformant client discovers the server, registers itself and starts the sign-in on its own. There is no API key to generate or store.
You log in and choose the scopes: read, write contacts, write campaigns, send campaigns, control automations, write leads. Leave out what you do not want.
The first time the assistant reaches for something new it stops and points you at Settings, Connected apps, to approve that one capability. After that it just works.
Every change shows up in your audit trail tagged with the tool and the name of the client. Revoke the connection, or a single capability, whenever you like.
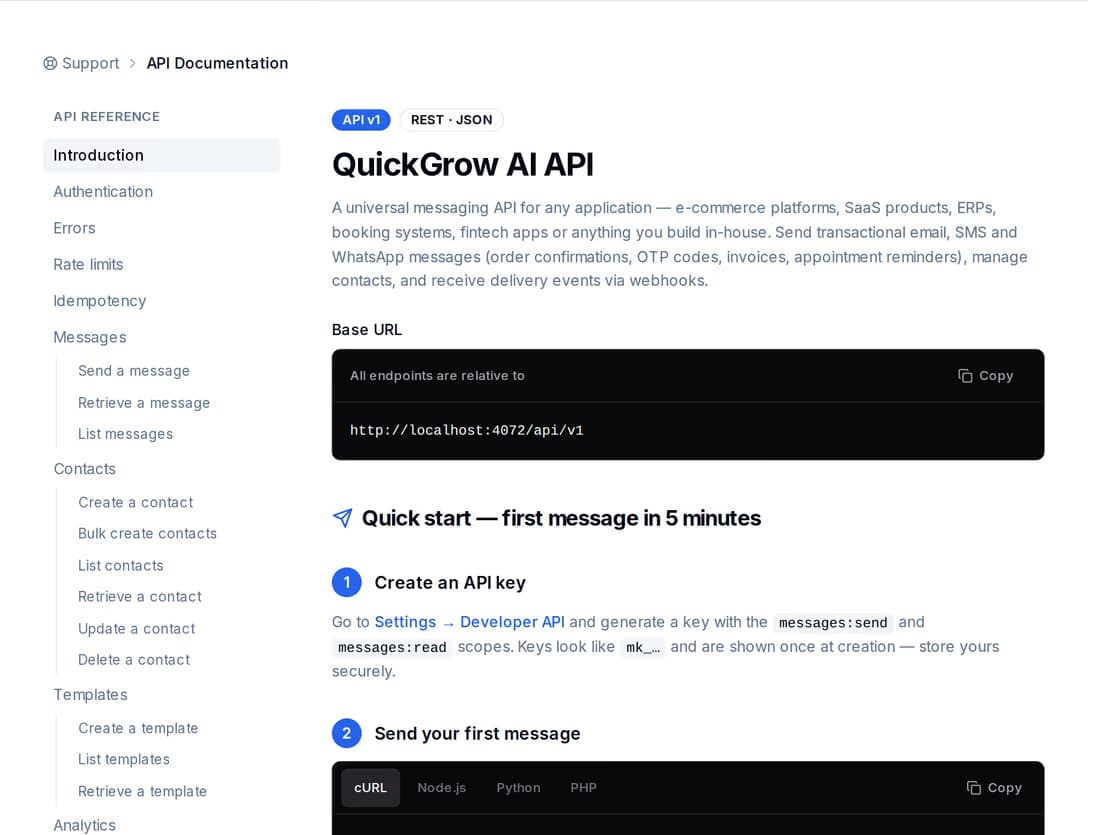
Authorisation is an ordinary OAuth code flow with PKCE and dynamic client registration, published for discovery at .well-known so a client can find it without being told. The tools themselves are served over the Model Context Protocol. If your assistant speaks those two things, it can connect today — and if you would rather write the code yourself, the same jobs are on the REST API.
Some of these look like missing features. They are decisions. An assistant is very good at doing what you asked slightly wrong, at speed, and the cheapest place to stop that is at the tool boundary.
The create tool only ever produces a draft. An assistant can build the whole campaign — audience, template, subject — and still cannot be the thing that decides to send it.
There is no edit tool and no delete tool. An assistant cannot quietly change a customer record or remove one, however confidently it thinks it should.
Every call names the brand it is for, and runs against that brand only. The separation is enforced by the database underneath, not by the tool asking nicely.
Any client that speaks the Model Context Protocol and can complete an OAuth sign-in — Claude, for example. Nothing about the server is specific to one vendor: the authorisation server and the tool endpoint are both discoverable, so a conformant client configures itself.
No, and there are two separate locks. The connection has to carry the send scope, and you have to have approved that capability once at Settings, Connected apps. Then every individual send or schedule stops and returns a preview with a one-time token that names the campaign and roughly how many people would get it. The token lasts ten minutes and works only for that campaign and that action.
Yes. Connect with the read scope alone and every write tool refuses with a message saying which scope it would have needed. That is a good way to start: let it answer questions about your campaigns for a week before you let it touch anything.
An assistant connects as you, not as an admin account. It inherits your membership and your brands, and nothing more — so what it can reach shrinks and grows with your own access.
Signs in as a person Writes are loggedConnect it read-only in an afternoon, watch what it gets right, then hand over one capability at a time.
 CyberCraft BangladeshQuickGrow AI
Run every channel from one platform. Bring your own SMTP, SMS gateway, and WhatsApp number — or use ours.
See pricing →